

Mastering SharePoint Group Permissions is essential for securing your data and ensuring productivity in the Microsoft 365 ecosystem. Are you confused about when to use Microsoft 365 groups versus native SharePoint groups? You’re not alone. This guide will demystify access management and show you exactly how to gain fine-tuned control over your sites.
365 Groups vs. SharePoint Groups: The Core Difference
One of the most common questions is, “What’s the difference between Microsoft 365 Groups and SharePoint Groups?”
1. Microsoft 365 Groups (The Hub)
When you create a Team Site, it automatically comes with an associated Microsoft 365 Group. This group acts as a central permissions hub that controls access to multiple services simultaneously:
- Email and Calendar (Outlook)
- Team chat (Microsoft Teams)
- Task management (Planner)
- The associated SharePoint Site
A 365 Group provides a streamlined, one-stop access management solution across the Microsoft 365 suite.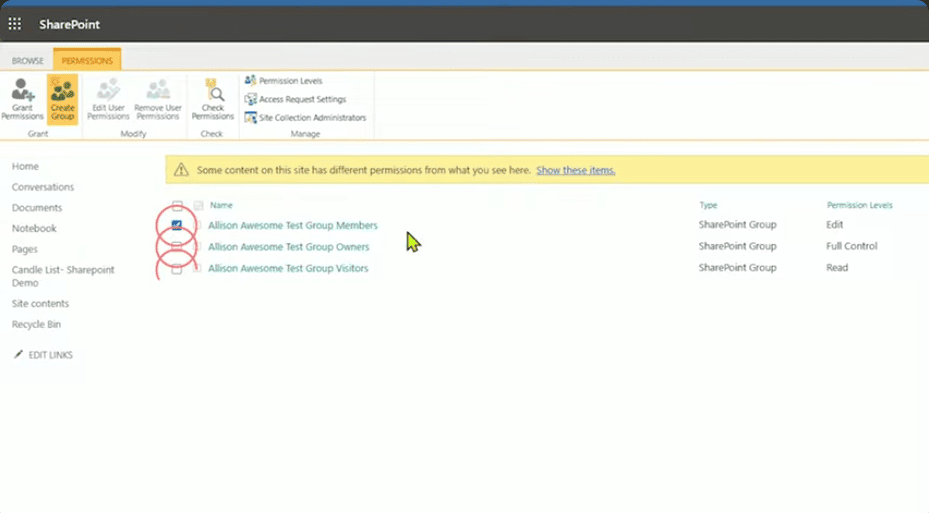
2. SharePoint Groups (Granular Control)
SharePoint Groups are the classic permission groups native to the SharePoint site itself. They provide granular control right within the SharePoint interface. By default, every modern SharePoint site includes three core groups: Owners, Members, and Visitors.
If you are managing a standalone Communication Site or need to create specific roles (like Reviewers or Contributors) with custom permissions, SharePoint Groups are essential.
| Feature | Microsoft 365 Group | SharePoint Group |
| Scope | Cross-App (Teams, Outlook, Planner, SharePoint) | Site-specific (SharePoint only) |
| Purpose | Streamlined access across the M365 ecosystem | Granular, site-specific roles/permissions |
| Control | Less granular (Owner, Member) | Highly customizable (Custom levels) |
Layering Permissions: Site-Only Access and Custom Roles
SharePoint allows you to layer permissions on top of the 365 Group structure:
- Site-Only Access: You can grant access just to the site content without providing access to the associated Teams, Outlook, or Planner.
- Advanced Permissions: You can navigate to Advanced Permission Settings to apply granular SharePoint permission levels (like Design, Edit, Contribute, or Read) directly to your 365 Group members, ensuring they can’t delete critical data or perform unauthorized actions.
Best Practices for Controlling External (Guest) Access
Controlling guest access is a critical security step for any organization.
1. Tenant-Level Policies (Admin Center)
As a SharePoint Administrator, you should move external sharing settings from the most permissive (like “Anyone”) down to the least permissive, such as “Existing guest” or “Only people in your organization.”
2. Site-Level Locking (Sensitive Data)
For departments handling sensitive data (like HR or Finance), you can completely disable guest sharing at the site level, even if the tenant settings are more open.
Auditing Tip: Always review the external user list in the Entra admin center (formerly Azure AD) to track exactly who has guest access across your entire tenant.
Final Thoughts and Next Steps
Mastering SharePoint permissions is all about using 365 Groups for broad access and SharePoint Groups for granular control. This layered approach maximizes productivity while maintaining rock-solid security.
Further Learning
Want to level up your Power BI and Power Platform skills?
Explore Power BI Training at Data Bear


